



A registrar’s legal obligations, abuse response, and ability to cooperate with European authorities should be central to every domain procurement decision.
In our previous article, we examined why a domain registrar’s jurisdiction matters to European organisations. That question becomes urgent when an organisation faces an active phishing campaign, needs registration data for an investigation, or must recover control of a business-critical domain.
At that point, the practical consequences of supplier selection become clear. Who can act? Which legal procedures apply? How quickly can the issue reach someone authorised to resolve it?
For EU public bodies and enterprises, a registrar’s response to those questions should carry more weight than a low annual registration fee.

Digital trust is becoming more important at the exact moment it is becoming harder to manage. As organisations expand their use of cloud services, machine identities, connected devices and AI, the number of certificates and cryptographic dependencies continues to grow. At the same time, shorter certificate lifecycles are leaving less room for manual processes and fragmented ownership.

The cybersecurity industry has become exceptionally good at detecting threats, but far less consistent at disrupting the infrastructure that enables them. As cybercriminals automate phishing, malware distribution, and fraudulent online services at unprecedented speed, abuse reporting and escalation processes often remain fragmented, manual, and slow. It's time to rethink how the industry collaborates to reduce cyber-enabled harm.
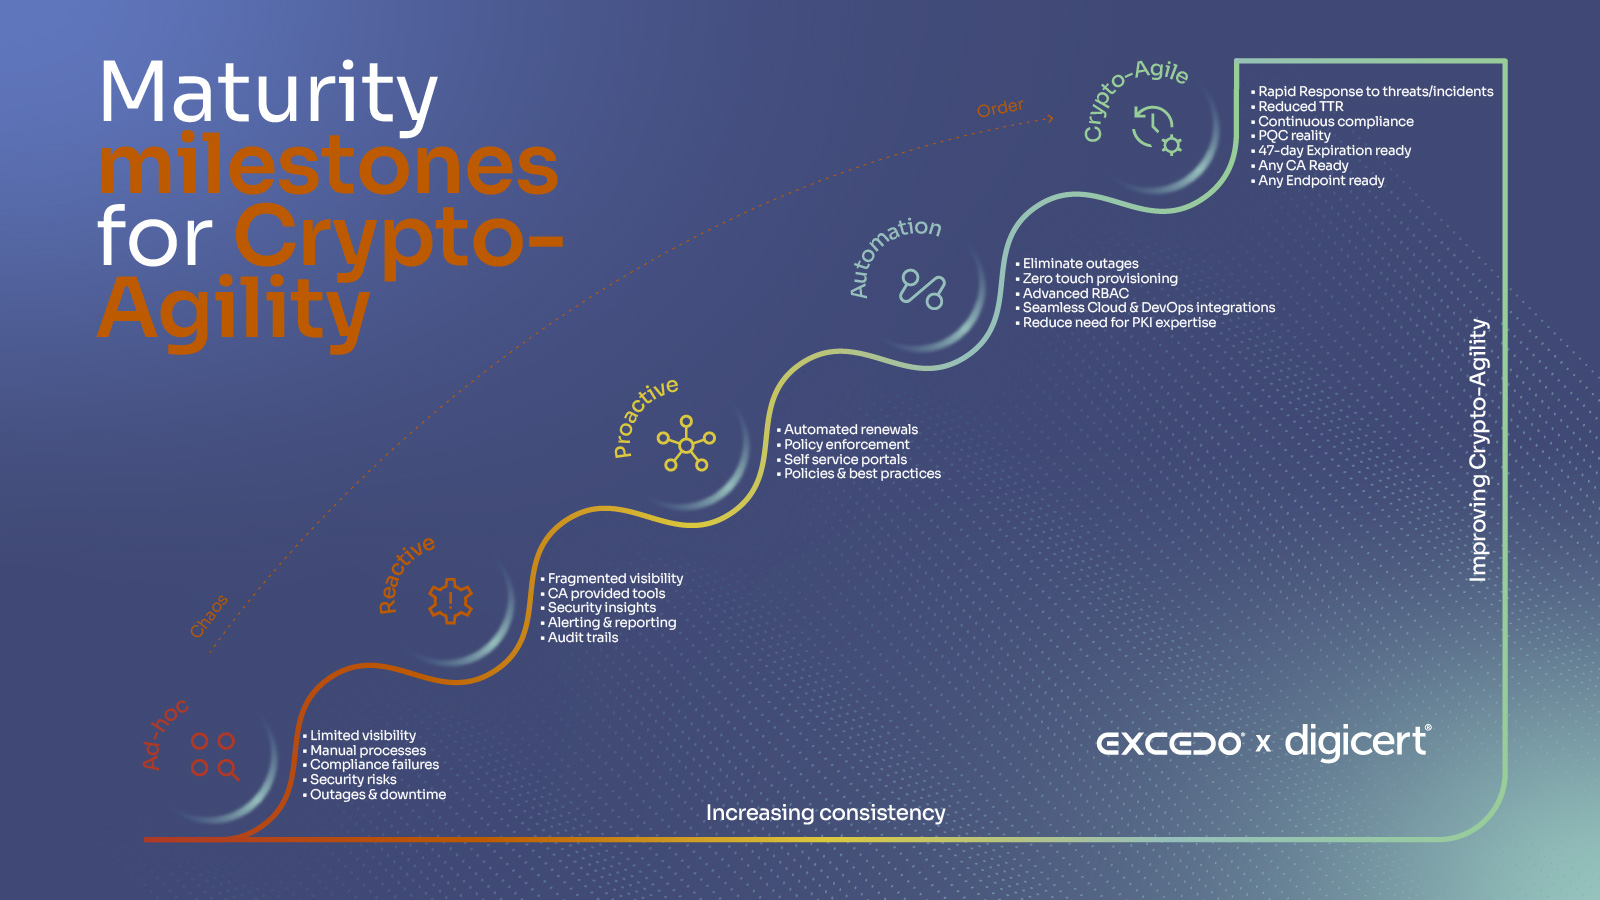
Digital transformation has dramatically increased the number of identities organizations must secure - users, devices, applications, APIs, and workloads. At the heart of this trust ecosystem lies Public Key Infrastructure (PKI). But PKI alone is no longer enough. As highlighted in Excedo’s perspective on digital trust, certificate automation has become a business imperative, not just an IT improvement. With certificate lifespans shrinking and threats evolving rapidly, organizations must move beyond managing certificates to becoming crypto-agile. This blog explores what crypto-agility means, why it matters, and how organizations can evolve through a structured maturity journey.
On 15 January 2026, Sweden's new Cyber Security Act (SFS 2025:1506) will come into force. The Act aims to achieve a high level of cyber security in society and implements the EU's NIS 2 Directive into Swedish law. This means that many organisations will face stricter requirements to improve their protection against cyber threats. The government has emphasised that municipalities and other organisations also need to ‘step up their game’ in their cybersecurity work – the new law will tighten the requirements for these actors. In this article, I summarise the purpose of the law, which public sector organisations are affected, the key obligations (particularly regarding security measures, incident reporting and training) and provide practical guidance ahead of its entry into force.

The upcoming Swedish Cybersecurity Act, which is based on the EU's NIS2 Directive, is often described as yet another heavy burden on organizations. But I would like to challenge that view. In fact, this law could mark the beginning of a new era: one in which cybersecurity is no longer a side issue, but a strategic opportunity and a key to competitiveness.

On August 23, 2025, IT supplier Miljödata AB was hit by a major cyberattack that knocked out important HR systems in over 160 Swedish municipalities and several regions. Miljödata supplies the Adato rehabilitation and HR system, which is used by 80% of Sweden's municipalities. The attack resulted in the theft of personal data for over one million Swedish citizens—including names, personal identification numbers, addresses, and contact details—linked to employees in municipalities such as Stockholm, Gothenburg, Linköping, and others.

Cloudflare is a linchpin of the modern Internet’s infrastructure, yet its “content-neutral” stance has repeatedly allowed phishing, malware, and extremist sites to hide behind its network. Security researchers warn that about 10.05% of all spam/malicious domains use Cloudflare’s nameservers, and that attackers routinely move flagged domains behind Cloudflare to “disguise the backend.”

Our previous articles on Cloudflare have highlighted how the company's global infrastructure can, paradoxically, protect cybercriminals and how Cloudflare's own processes fall short when it comes to dealing with abuse. We have seen that Cloudflare's free platforms for pages and scripts are widely used for phishing and spreading malware, and that abuse reports are often met with automatic rejections instead of swift action. Critics have pointed to a ‘blind spot’ at Cloudflare: that the company's enormous reach and business model sometimes outweigh proactive security.

Cloudflare sits behind one in five websites, promising speed, and security. But the same infrastructure now hides an industrial scale phishing economy. For six (6) months we tracked more than +600 fake tiquetesbaratos.com fraud domains - multiple hosted on pages.dev or workers.dev and fraud domains levering the Cloudflare reverse-proxy DNS services. Abuse reports met the same copy paste dismissal: “Unable to confirm phishing.” This article investigates why Cloudflare’s processes fail, how that failure fuels criminals, and what lawmakers must do next.

What is new since Excedo’s October 2024 primer on KYC for domain name registrants? Why Article 28 still matters.

The NIS2 Directive places new requirements on domain name registrars to get accurate information on registrants in order to minimise the anonymity that enables cybercrime.

The requirements of the NIS2 Directive are extensive and address many different aspects of digital security, including email security. For organizations to meet the email security standards set by NIS2, they need a correctly configured DMARC policy.

The NIS2 Directive will raise digital security levels across the EU. Although its jurisdiction spans across borders, individual countries have a say in how the requirements will be implemented locally and if they want to go above and beyond the security baseline set by NIS2.

Jan Stenbecks torg 17
164 40 KISTA
SWEDEN