Blog
Articles, interviews, and useful tips to help you with everything from starting a Premium Anycast DNS project to securing your organization against cyberthreats.


Articles, interviews, and useful tips to help you with everything from starting a Premium Anycast DNS project to securing your organization against cyberthreats.

A registrar’s legal obligations, abuse response, and ability to cooperate with European authorities should be central to every domain procurement decision.
In our previous article, we examined why a domain registrar’s jurisdiction matters to European organisations. That question becomes urgent when an organisation faces an active phishing campaign, needs registration data for an investigation, or must recover control of a business-critical domain.
At that point, the practical consequences of supplier selection become clear. Who can act? Which legal procedures apply? How quickly can the issue reach someone authorised to resolve it?
For EU public bodies and enterprises, a registrar’s response to those questions should carry more weight than a low annual registration fee.

Digital trust is becoming more important at the exact moment it is becoming harder to manage. As organisations expand their use of cloud services, machine identities, connected devices and AI, the number of certificates and cryptographic dependencies continues to grow. At the same time, shorter certificate lifecycles are leaving less room for manual processes and fragmented ownership.

The cybersecurity industry has become exceptionally good at detecting threats, but far less consistent at disrupting the infrastructure that enables them. As cybercriminals automate phishing, malware distribution, and fraudulent online services at unprecedented speed, abuse reporting and escalation processes often remain fragmented, manual, and slow. It's time to rethink how the industry collaborates to reduce cyber-enabled harm.
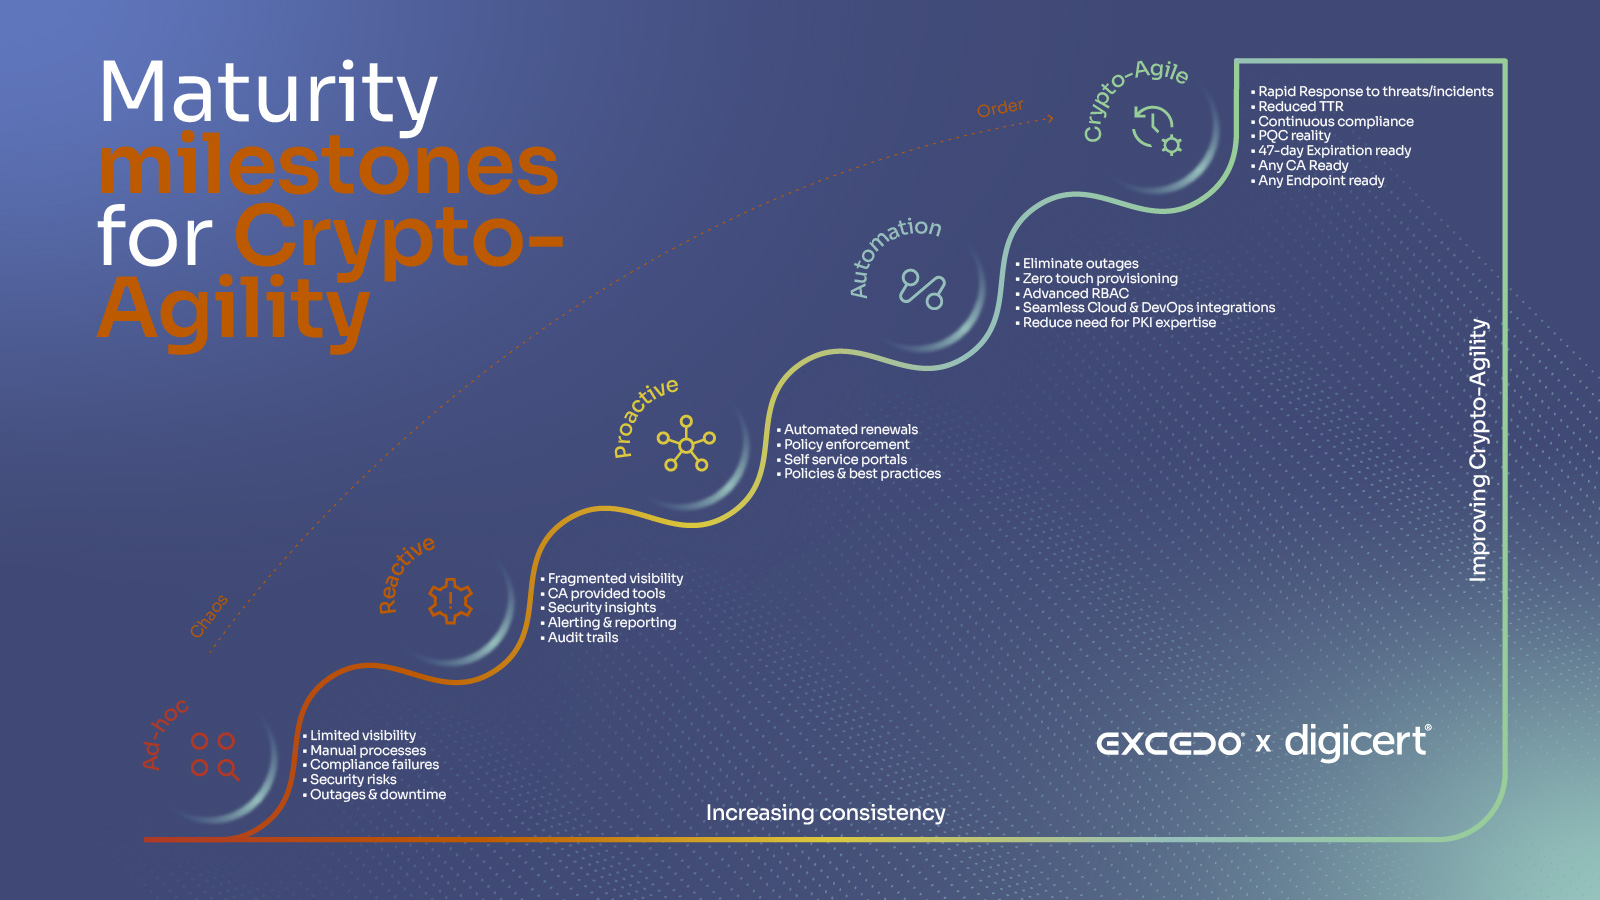
Digital transformation has dramatically increased the number of identities organizations must secure - users, devices, applications, APIs, and workloads. At the heart of this trust ecosystem lies Public Key Infrastructure (PKI). But PKI alone is no longer enough. As highlighted in Excedo’s perspective on digital trust, certificate automation has become a business imperative, not just an IT improvement. With certificate lifespans shrinking and threats evolving rapidly, organizations must move beyond managing certificates to becoming crypto-agile. This blog explores what crypto-agility means, why it matters, and how organizations can evolve through a structured maturity journey.
The default settings of most major email providers have for a long time not been enough to stop email threats from reaching inboxes. But that is now changing with Google and Yahoo's new email security requirements, including the mandatory implementation of DMARC.
A DMARC (Domain-based Message Authentication, Reporting, and Conformance) policy is a key part of organizational email security. It prevents email threats from reaching your employees and users, and it is now a requirement by major email providers like Gmail and Yahoo.

Jan Stenbecks torg 17
164 40 KISTA
SWEDEN